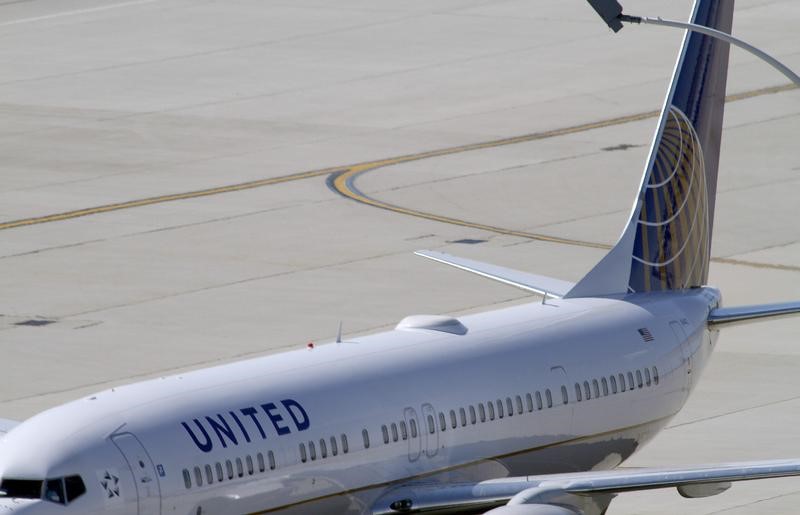
Now here’s a rewards program Julian Assange could love. United Airlines has confirmed that it paid 1 million frequent flier miles each to two hackers who found serious flaws and security breaches in its computer systems.
Related: Millions of Samsung Galaxy Phones May Be Vulnerable to Hackers
This past May, United started a “bug bounty” program to find loopholes in its security, but it’s hardly the first corporate entity to do so. Google, Facebook and Yahoo all offer rewards or incentives to hackers who report bugs to them privately. Netscape engineer Jarrett Ridlinghafer is largely credited with coming up with the concept of rewarding good, or “white hat,” hackers for trouble-shooting in 1995.
Jordan Wiens, founder of cybersecurity company Vector 35, was one of two winners to claim a million airline miles for his prize. He posted a screenshot of his mileage account on Twitter. (He submitted the bug on May 15, got a response on May 19, a validation notice on June 24 and then the payout on July 10.) A second bug he reported won a lesser prize of 250,000 miles. Kyle Lovett from Montgomery, Calif., was the other million-mile winner. Lovett Tweeted that he will use some of the miles to fly out his mother and brother to California.
Wow! @united really paid out! Got a million miles for my bug bounty submissions! Very cool. pic.twitter.com/CEclmhmyUq
— Jordan Wiens (@psifertex) July 10, 2015
No doubt the airline saved a ton of money in preventing computer issues. In recent months United has had to ground it flights twice as a result of computer system glitches. On June 2, an automation issue affected 150 flights, or 8 percent of its morning schedule. On July 8, a network connectivity issue due to a router malfunction locked up its reservations system and grounded thousands of flights worldwide.
Looks like the airline has more miles to dole out, too: Twitter was full of happy pronouncement from hackers claiming smaller prizes and begging Delta to do the same.